The nostalgic era of casually tossing a jpeg of your driver's license into a web form evaporated. We now face a much harsher landscape. A modern consumer cannot spin up a basic banking app, clear a digital border check, or view adult material without surviving a high-friction gauntlet. Consumer platforms currently operate deep inside a hostile warzone. Regulators hold companies at gunpoint, demanding they hoard highly sensitive personally identifiable information (PII). A nightmare scenario unfolds the instant those records hit a centralized server. The accumulation of KYC material acts as a massive beacon for cyber syndicates. Global watchdogs want full visibility into user histories; simultaneously, privacy frameworks will financially decapitate a business if those same records leak.
Registration flows suffer immensely under this pressure. Abandonment rates hover around 34 percent for complex onboardings. Developers finally realize that demanding more friction is a losing strategy. Modern digital trust bypasses human review entirely. The ecosystem relies on advanced cryptography, localized edge computing, and cold hardware attestation.
The Toxic Asset Problem
Threat actors then discovered generative AI, and the entire house of cards collapsed. Fraud rings shifted decisively away from manual credential stuffing months ago. Impersonation now fuels over 85 percent of all malicious activity across digital platforms. We are dealing with synthetic identities on an industrial scale.
Synthetic profiles—where someone glues a stolen social security number to a completely fake name and an AI-generated face—make up nearly a quarter of all attacks. These malicious accounts are a nightmare for risk teams because they do not trigger immediate consumer complaints. The fake profiles just sit on servers, quietly aging and building fake credit histories. A massive "bust-out" fraud eventually occurs, draining billions from the financial system overnight. The stakes for proper identity checks have never been higher.
Deepfakes and the Death of the Selfie
Legacy software used to beg a new signup to blink, smile, or look sideways—a desperate bid to catch a printed photo or a latex mask. Let's be real about the street value of that defense today. It is completely useless. Bad actors simply spin up a synthetic face that blinks and grimaces perfectly on command, entirely bypassing the old logic. The fatal flaw of standard liveness was a blind assumption of hardware integrity. Algorithms evaluated the video feed and naively trusted that the footage came from the physical camera lens of an uncompromised smartphone.
Criminals gave up on fooling the physical camera lens years ago. The entire war now happens at the software layer. Virtual camera drivers and emulators allow attackers to inject deepfakes straight into the data stream. An injected synthetic video intercepts the liveness prompt, performs the requested action, and glides right past the verification engine.
Modern defenses run entirely on baseline paranoia. The architecture simply assumes the phone in your hand is already breached. Runtime monitors aggressively hunt for hijacked camera drivers, while core protocols verify the application itself hasn't been stripped down or hot-wired by a fraudster. Verification engines no longer care about the face in the picture; they interrogate the exact pathway the pixels took to reach the processor.
The Regulatory Vise Grip on the App Store
Legislators completely lost patience with the internet's honor system and weaponized child safety rules. The fallout is an operational bloodbath for product teams. A unified federal rule does not exist in the United States. State capitals instead pass wildly conflicting mandates every few months. Texas and Louisiana push severe ID-based validation laws for adult content, while California hands out aggressive fines for profiling minors. The European Union's Digital Services Act looms overhead with threats to fine companies up to 6 percent of global turnover for systemic age assurance failures.
Friction is especially brutal for platforms that tie constant geolocation to identity checks. Architects behind sophisticated gaming infrastructure like the one found at DraftKings Casino face immense pressure to utilize state-of-the-art encryption to process sensitive KYC data in real-time. Operators run dynamic validation loops continuously to ensure compliance. Latency instantly kills user retention during a live session. Product leaders are forced to fundamentally rethink how data moves across their networks to maintain any illusion of speed.
Cryptographic Bunkers and Cold Steel
Architectural consensus shifted hard toward decentralized, heavily encrypted vaults. Microservices have no business touching raw identity data. Storage of unencrypted PII in an active database is essentially professional negligence today. Vaulted tokenization offers the only viable path forward. An edge gateway intercepts sensitive documents before they ever reach the primary cloud. Raw files get locked away inside an isolated vault, handing the active application nothing but a useless cryptographic reference token.
Hardware Security Modules (HSMs)—tamper-resistant steel boxes humming in server racks—hold the only keys capable of reversing that token. Criminals who breach the active environment just walk away with meaningless alphanumeric strings.
We are also watching a massive shift toward edge biometric processing. Older setups streamed live video feeds to central servers, creating immense network drag and building toxic centralized repositories of facial templates. Leading SDKs pushed all that heavy neural network processing down to the local smartphone chip. The user's device extracts the biometric features and matches the selfie against the ID document in real-time. A cryptographically signed binary outcome is the only thing the backend ever sees. Your actual face stays exactly where it belongs—trapped in local memory.
The Unforgiving Math of Zero-Knowledge
The best way to survive a data breach is to refuse to collect the underlying data in the first place. Zero-Knowledge Proofs (ZKPs) and Verifiable Credentials are rewriting the internet to do exactly that. The eIDAS 2.0 framework pushed the European Union to require government-backed digital wallets for citizens by the end of 2026. People store their verified attributes locally now.
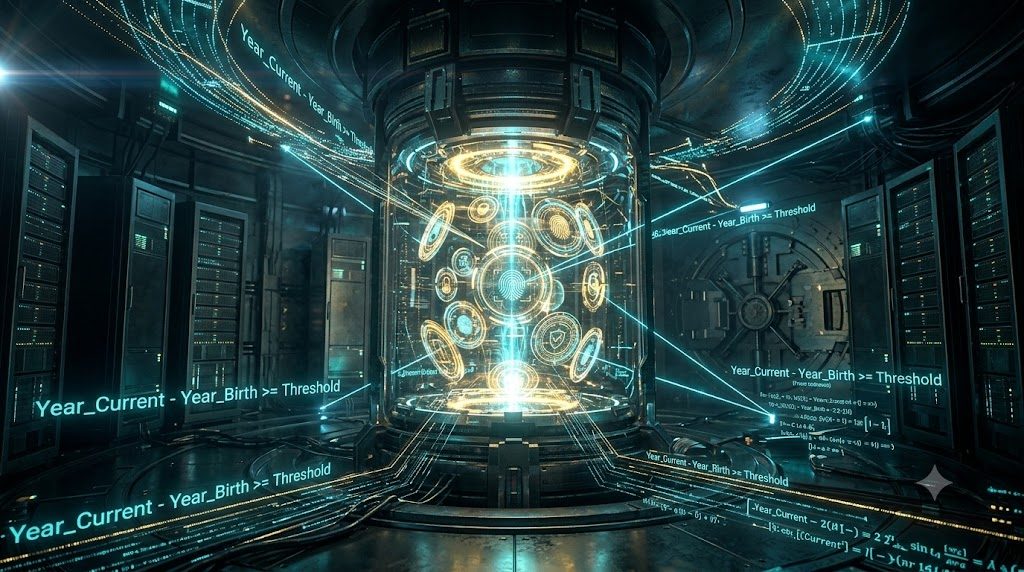
Nobody actually needs to surrender their physical passport to prove they can buy a beer. A decentralized identity wallet runs the necessary algebra locally. The magic here is a Zero-Knowledge Proof. A user effectively convinces a backend server that a condition is met, yet no underlying context changes hands. The cryptography built into zk-SNARKs limits the transaction to a simple yes-or-no check on age. The rest of your life remains completely off the grid.
Backend servers traditionally choked on this level of complex math. Hardware engineers finally cracked the performance bottleneck. A standard smartphone now crunches these proofs in a fraction of a second. The app consumes a micro-payload—maybe 256 bytes—and clears the user instantly.
The reality is stark. Corporations face a guaranteed death sentence if they hoard vast lakes of user data. Customers want frictionless access without sacrificing their digital sovereignty. The combination of hardware tokenization and localized zero-knowledge cryptography burns down the honeypots that syndicates relied on for twenty years. Trust is no longer a human looking at a photo. It is an unyielding mathematical threshold.